AI Agent Authorization & Boundaries Policy
What an agent can do alone, what needs approval, and what it must never do — defined before deployment, not after an incident.
Preview
Real screenshots of the file you receive. The full document includes much more content.
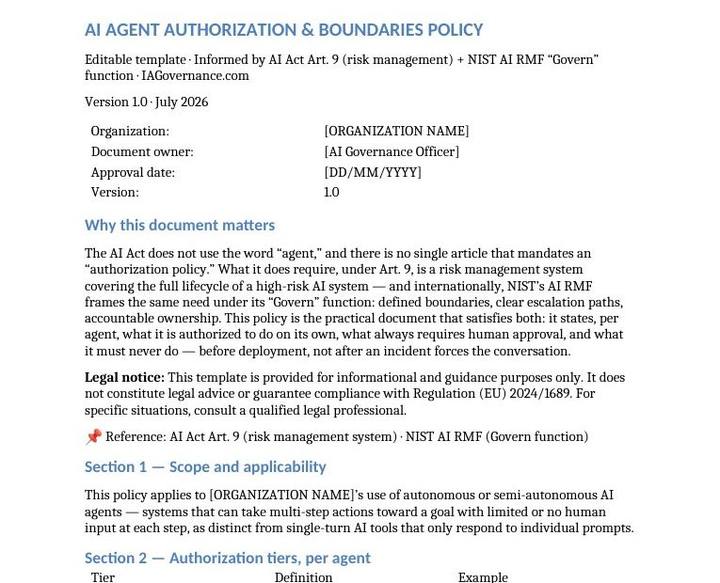
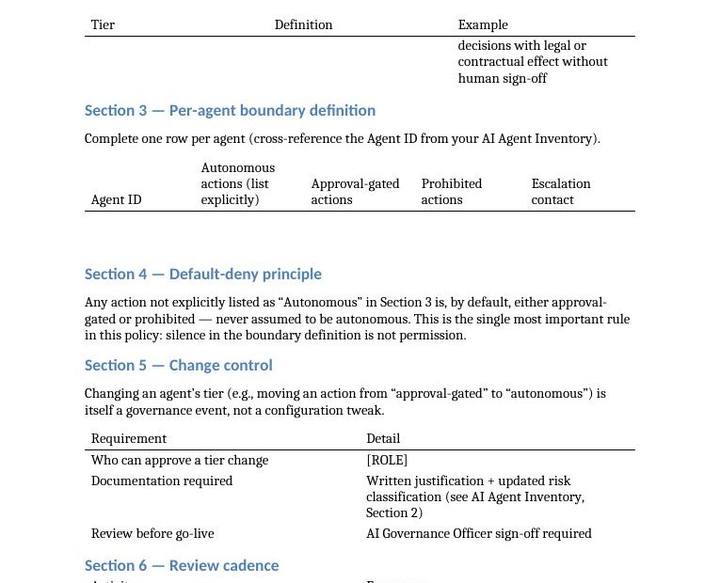
What's included
- Editable Word template
- 3 authorization tiers per agent
- Default-deny principle
- Legal Notice
Why this document exists
The AI Act doesn't use the word "agent," and no article mandates an "authorization policy." What Art. 9 does require is a risk management system covering the full lifecycle of a high-risk system — and internationally, NIST's AI RMF frames the same need under its "Govern" function. This policy is the practical document that satisfies both: it states, per agent, what it can do alone, what always needs human approval, and what it must never do.
Frequently asked questions
Who is this policy for?
Teams deploying AI agents that can act on real systems (sending emails, modifying records, approving transactions) who need clear boundaries before an incident forces the conversation.
Does it replace legal advice?
No. It's a working template that organizes and speeds up the compliance process, but does not constitute legal advice or guarantee compliance with Regulation (EU) 2024/1689 — see the included Legal Notice.
What format is it delivered in?
Instant download after purchase: editable Word template, plus the Legal Notice.