Encryption & Key Management Policy
What gets encrypted, to what standard, and who manages the keys through their full lifecycle — the governance document missing between "we have RBAC" and "we actually protect the data".

Preview
Real screenshots of the file you receive. The full document includes much more content.
What's included
- Word with the full policy: what data must be encrypted in transit and at rest based on its classification level, minimum acceptable standards, key lifecycle management (generation, rotation, revocation, custody)
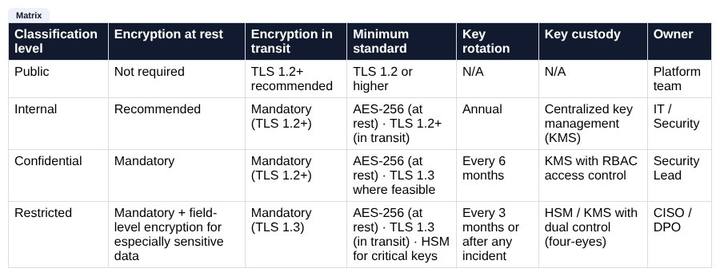
- Decision matrix: what encryption level corresponds to each data classification level
- Legal Notice
Why this document exists
Many companies have encryption enabled by default with their cloud providers, but have no document explicitly stating what's required, who's responsible for keys, or what happens when a key must be rotated or revoked after an employee with access leaves. Without that policy, any audit or client asking "how do you manage encryption keys?" gets an improvised answer instead of a documented process.
Frequently asked questions
Does this replace the technical encryption implementation?
No. It's the governance document that defines what standards and processes the technical team must follow — it doesn't replace implementation in your systems.
Do I need technical cryptography knowledge to use this template?
Not to adapt the document itself, but IT/Security should review the specific technical standards before final approval.
Does this replace legal advice?
No. It's a policy template, but it doesn't constitute legal or technical advice, nor does it guarantee regulatory compliance on its own — see the included Legal Notice.
What format is it delivered in?
Word with the full policy, plus the Legal Notice.